Next-Gen SIEM & SOARCloud Ecosystem
CyberHall ingests multi-layer telemetry from endpoints, networks, cloud environments, and identity providers, correlating events in real-time within a single, proprietary SIEM/SOAR platform[cite: 171, 228, 278, 281].
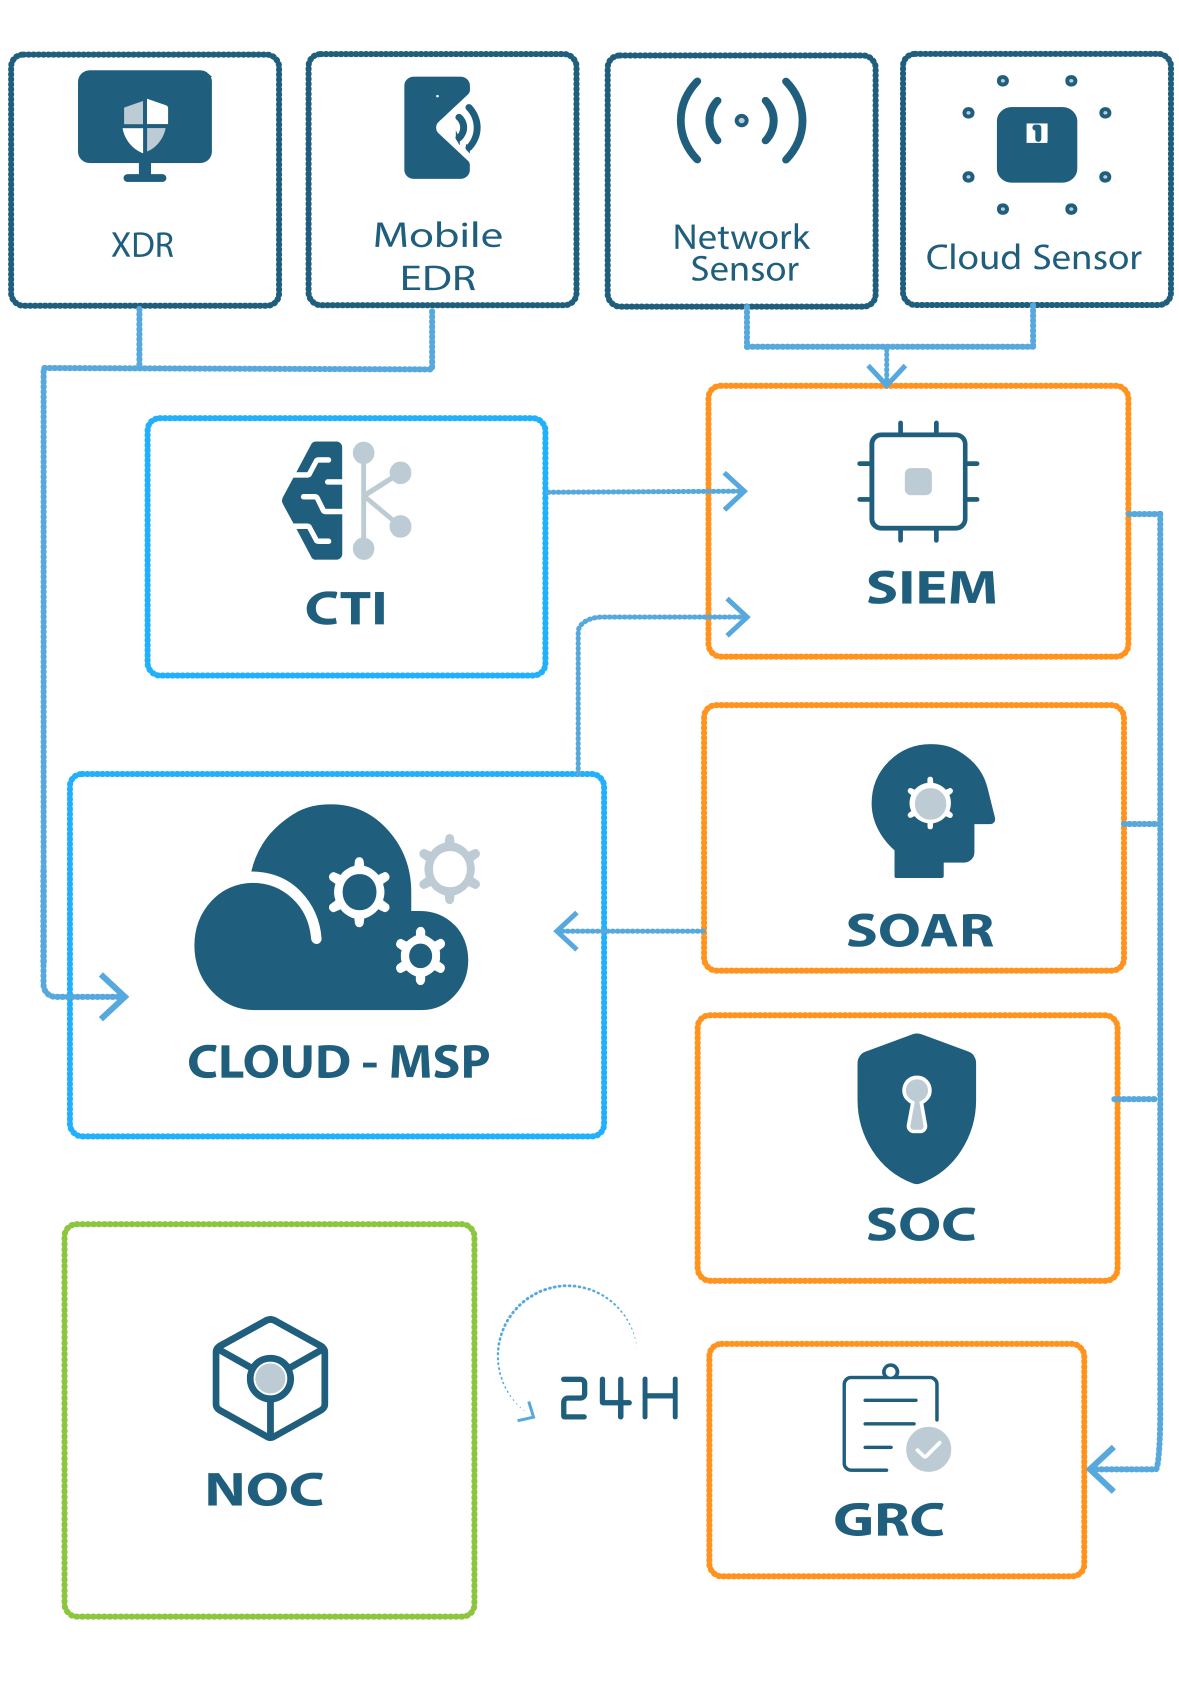
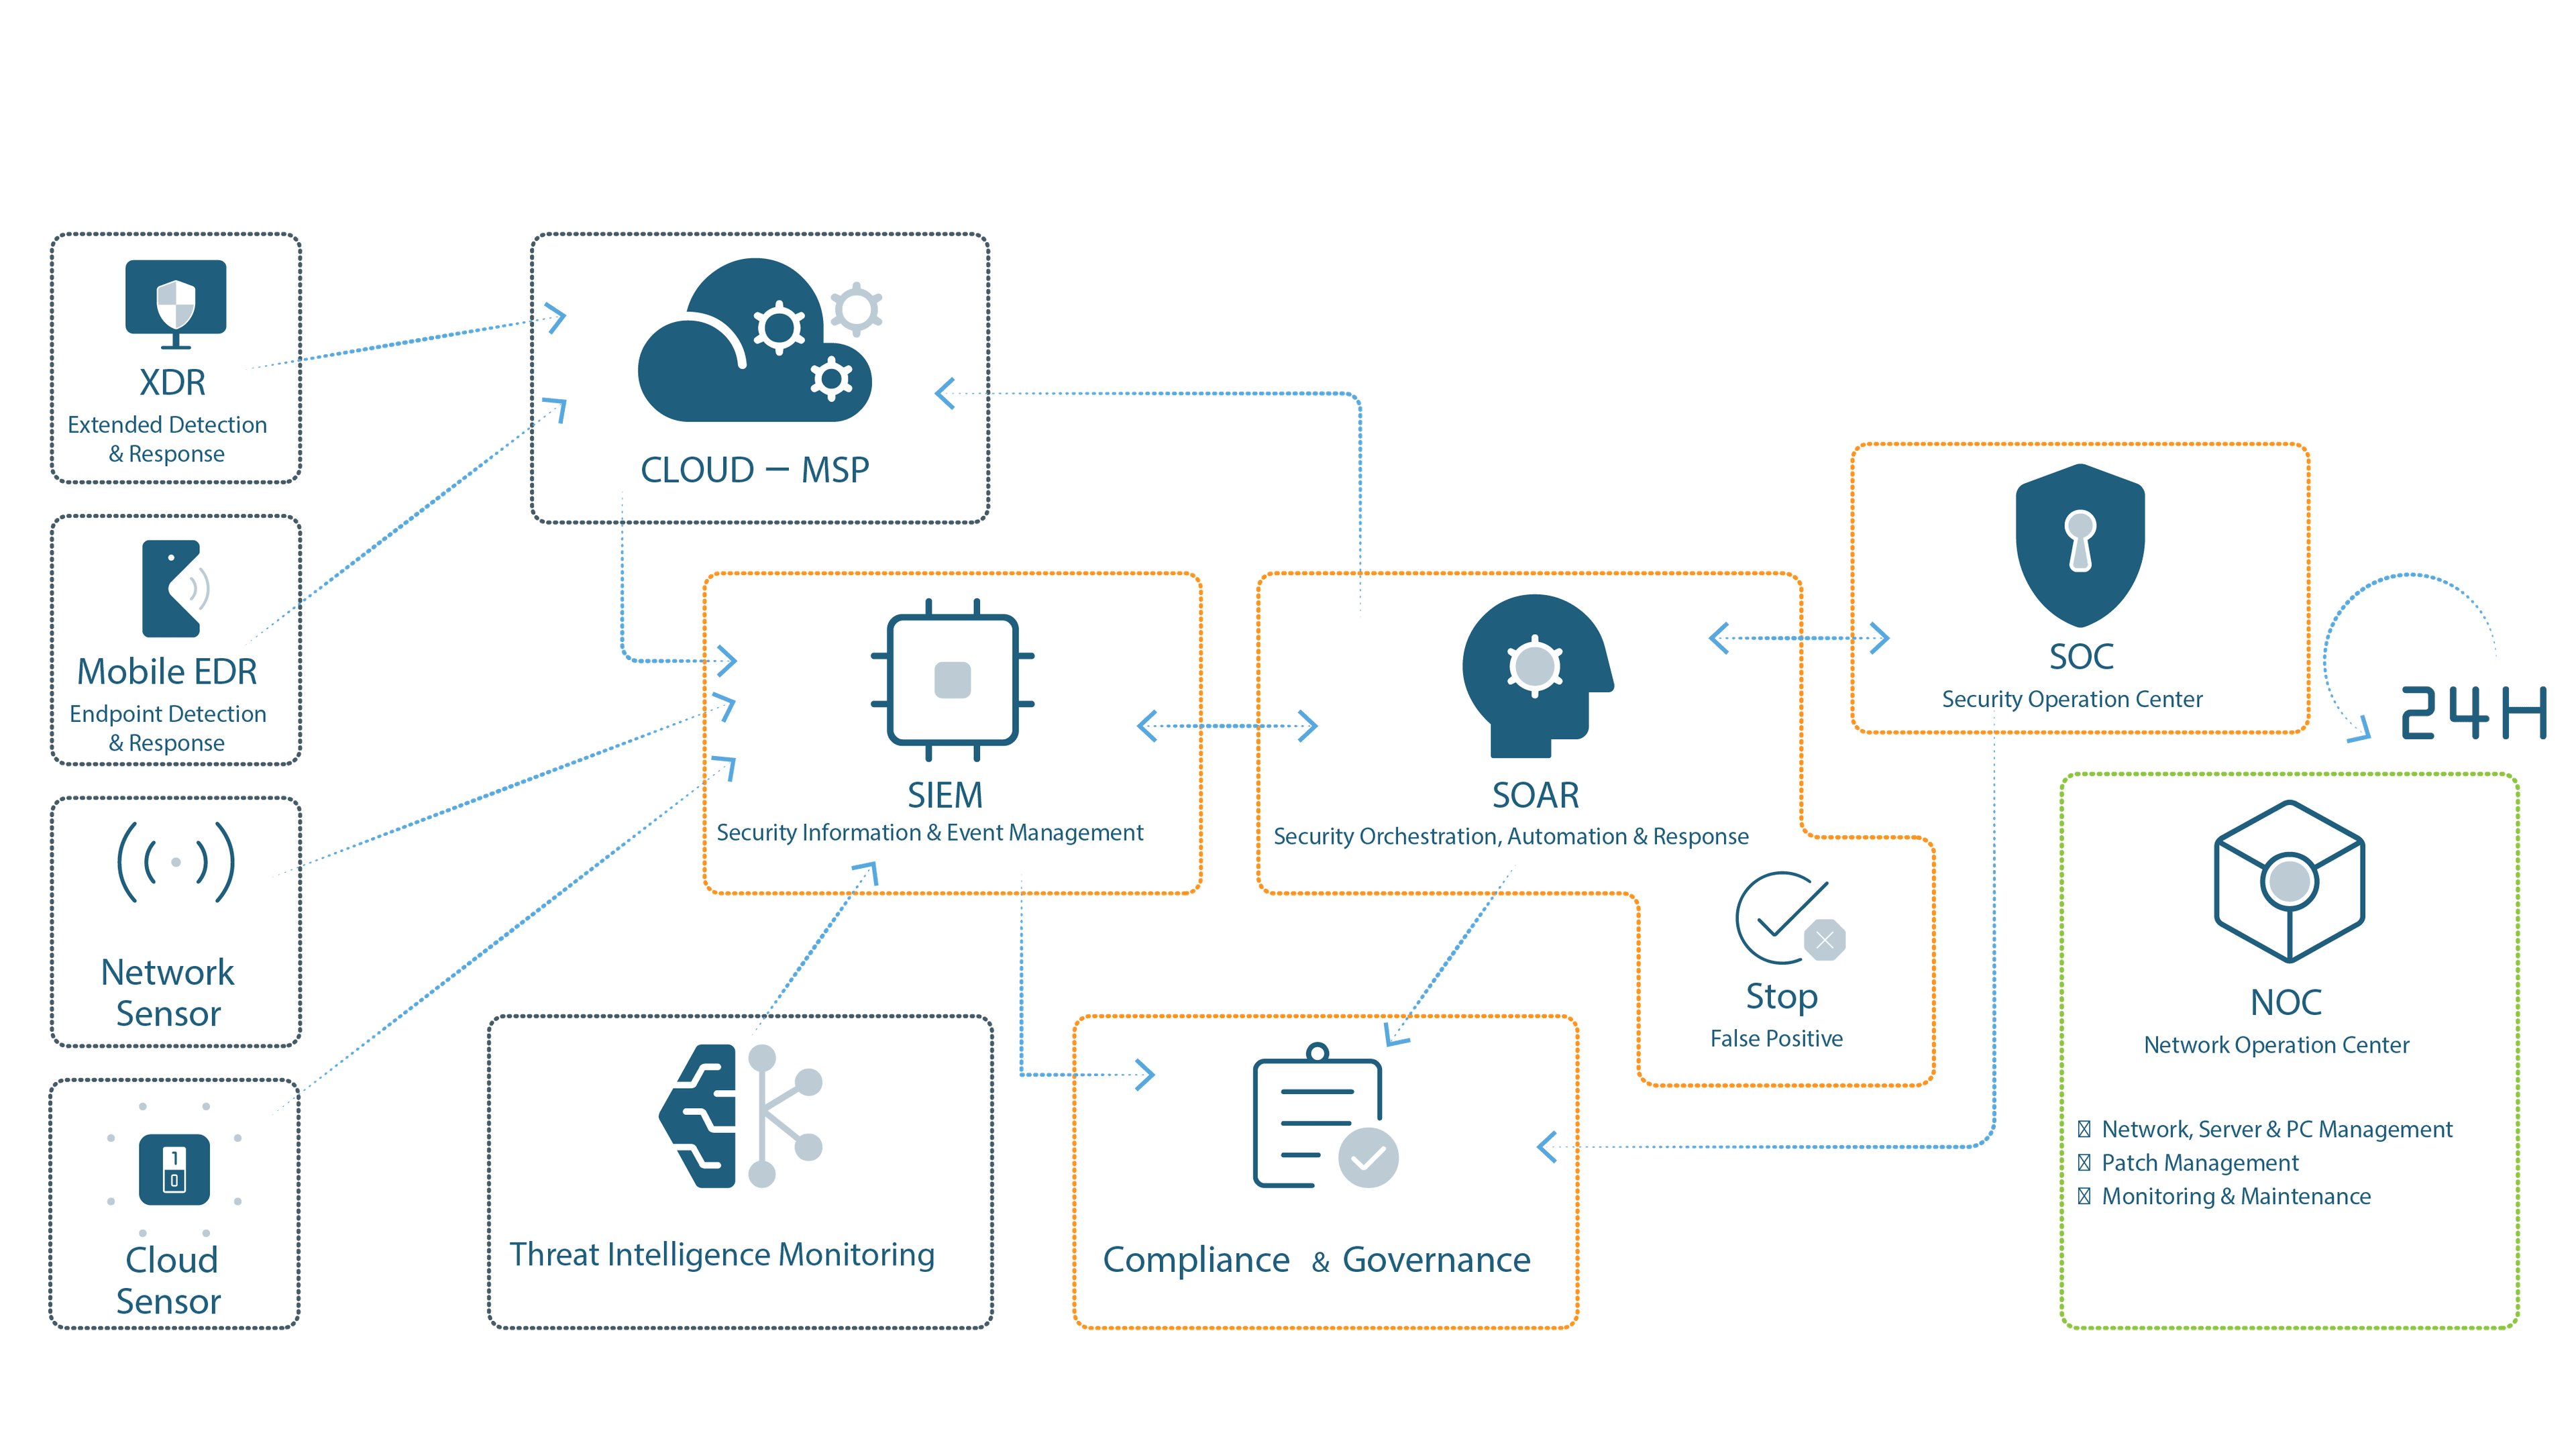
Unified Data Collection (Multi-Layer Data)
Competitors rely on monitoring either the network OR endpoints. CyberHall's intelligent sensors cover every organizational perimeter[cite: 95, 318].
Endpoint & Mobile (XDR)
Lightweight, non-intrusive agents constantly monitor workstations, servers, and mobile devices (Android/iOS), blocking local attack vectors and behavioral anomalies[cite: 220, 221, 225, 270].
Network & OT Monitoring
Deep inspection of network traffic via physical or virtual probes (SPAN/TAP). Ideal for protecting critical infrastructure and industrial networks (Operational Technology)[cite: 95, 235, 237, 239].
Cloud & Identity Layer
Native API integration with Microsoft 365, Google Workspace, AWS, Azure, and leading Identity Providers[cite: 185]. Immediate tracking of anomalous logins or data exfiltration attempts.
Intelligent Multi-Source Correlation
Traditional software dumps thousands of unmanageable alerts onto IT Managers[cite: 28, 29, 299, 300]. CyberHall's SIEM engine gathers isolated telemetry and fuses it into a single security context[cite: 185, 278, 279].
90% Noise Reduction
Raw data is automatically enriched and validated, eliminating false positives before they ever reach an analyst's attention[cite: 28, 29, 32, 288, 300].
Automated SOAR Playbooks
Upon detecting a true threat (e.g., Ransomware), the SOAR triggers automated host-isolation workflows to reduce response time to zero[cite: 185, 230, 256, 280, 281].
// CyberHall SIEM Correlator active...
Compare our services
Three levels of coverage, from continuous SOC monitoring to complete compliance management.
A 24/7/365 SOC service focused on endpoint monitoring through integration with EDR solutions. It includes security event detection, analysis, and management, supported by automated playbooks, automation capabilities (SOAR), data enrichment, and intelligent analysis support for prioritization and noise reduction. The service is limited to the endpoint perimeter and the data provided by the EDR, ensuring structured alert management and a timely response to detected events.
An add-on to Core SOC that extends security event monitoring and correlation across the entire corporate IT ecosystem. In addition to endpoints, it integrates network infrastructure, firewalls, cloud environments, and collaboration platforms, providing greater visibility and context for security events. It includes advanced capabilities such as threat intelligence, custom use cases, and response process automation, improving detection capabilities and reducing false positives.
A dashboard and reporting platform for continuous monitoring of the organization’s security posture. It aggregates data from security systems, providing visibility into risks, events, and the status of remediation activities. It includes risk indicators (risk scores), audit reporting, and support for key regulatory requirements (e.g. NIS2, GDPR, DORA), together with a library of templates and documentation (policies, procedures, incident response) and tracking tools for compliance management.
Explore the comparison table to see all Cyberhall platform features, divided by CORE SOC, PREMIUM SOC, and COMPLIANCE DASHBOARD.
Monitoring & Detection
24/7 monitoringEnterprise
Continuous security event monitoring with 24/7/365 coverage
Endpoint log collection (EDR)Enterprise
Ingestion and analysis of events from endpoints and servers
Alert triage and managementEnterprise
SOC-led analysis, classification, and handling of alerts
Network event monitoringEnterprise
Collection and analysis of events from network infrastructure
Cloud environment integrationEnterprise
Monitoring of events and activity across cloud and collaboration platforms
Multi-source correlationEnterprise
Correlation of events from multiple systems to identify complex threats
Threat IntelligenceEnterprise
Integration and analysis of intelligence sources to identify external threats and support proactive detection activities.
Response & Automation
Response playbooksEnterprise
Standardized procedures for incident handling
SOAR – AutomationEnterprise
Automation of response workflows, data enrichment, and correlation
Data enrichmentEnterprise
Automatic enrichment of events with contextual information
AI supportEnterprise
Support for event analysis through intelligent models for automation, prioritization, correlation, and noise reduction.
False-positive reductionEnterprise
Ongoing optimization to improve alert quality
Incident Response ManagementEnterprise
Management of security incidents, from identification through containment.
Behavioural analysisEnterprise
Identification of anomalies based on user and system behaviour
Custom use casesEnterprise
Detection rules and scenarios tailored to the customer's context
Visibility & Reporting
Security posture visibilityStandard
An overview of security status and events
Risk indicators (Risk Score)Standard
Summary metrics for assessing risk levels
Remediation statusStandard
Monitoring of corrective actions and activities
Audit reportingStandard
Structured reports for reviews and controls
KPI & Executive Reporting
Dashboards and concise reports for management and non-technical stakeholders.
Compliance & Documentation
Regulatory support
Alignment with standards including NIS2, ISO 27001, and GDPR
Document library
Templates and documentation, including policies, procedures, and IRPs
Document Lifecycle Management
Management of versioning, updates, and the status of security documents.
Compliance Audit
Complete tracking of processes, activities, and events to support audits and reviews.
Capabilities delivered through EDR integration, with visibility and operational coverage limited to data and events originating from endpoints.
Features included in the base service, with coverage limited to the endpoint perimeter (EDR) and predefined, non-custom configurations.
Comprehensive, advanced, and tailored capabilities.
Want to see the architecture in action?
Discover how our engineers seamlessy integrate the CyberHall platform into your current infrastructure with zero downtime[cite: 106, 110, 304, 308].